Showing posts with label Ransomware. Show all posts

VanHelsing Unleashed: The RaaS That Targets Windows, Linux, BSD, ARM and VMware ESXi


VanHelsing RaaS: a cross-platform ransomware that weaponizes affiliates to hit Windows, Linux, BSD, ARM and ESXi

VanHelsing has emerged as a sophisticated ransomware-as-a-service (RaaS) operation that changes the rules for cross-platform attackers. First observed on March 7, 2025, VanHelsing provides a fully packaged service to criminal affiliates: a $5,000 deposit to join, an 80% cut of ransom payments for affiliates, and a user-friendly control panel to orchestrate attacks across heterogeneous environments.

New RaaS Operation ‘Gentlemen’s’ Surfaces, Expanding Attacks to Windows, Linux, and ESXi Systems


Gentlemen’s” RaaS: a new cross-platform ransomware service advertised on hacking forums

 A new affiliate-style ransomware-as-a-service called Gentlemen’s, promoted by actor zeta88, brings purpose-built lockers for Windows, Linux, ESXi and more — and a generous 90/10 revenue split that could accelerate adoption.

Ransomware Group Exploits Critical Windows CLFS Zero-Day Vulnerability


Critical Windows CLFS Zero-Day Exploited by Ransomware Group — Patch Now!

A new zero-day vulnerability in Microsoft Windows has come under active exploitation by a sophisticated ransomware group, prompting an urgent security response from Microsoft. The flaw, identified as CVE-2025-29824, affects the Common Log File System (CLFS) and has already been used in targeted attacks across multiple industries and countries.

Russia Cracks Down on Cybercrime: Wazawaka Arrested for Ransomware Links


Russia Arrests Infamous Cybercriminal Mikhail Matveev, Known as Wazawaka, for Ransomware Ties

Russian authorities have arrested Mikhail Pavlovich Matveev, also known by aliases such as Wazawaka, Uhodiransomwar, m1x, and Boriselcin, on charges of developing ransomware and participating in multiple hacking groups.

Cybercrime Crackdown: The Fall of Phobos Ransomware's Admin


Phobos Ransomware Admin Extradited: A Major Win in the Fight Against Cybercrime

In a significant development in international cybercrime enforcement, Evgenii Ptitsyn, a Russian national and suspected administrator of the notorious Phobos ransomware operation, has been extradited from South Korea to face charges in the United States. This marks a pivotal moment in efforts to combat ransomware-as-a-service (RaaS) platforms that have wreaked havoc globally.

Journey of Open Source Ransomware converted into deadly wiper malware


Fortinet discovers a Cryptonite sample in the wild that never provides decryption capabilities. Cryptonite is an open-source ransomware toolkit developed initially by CYBERDEVILZ group with very few contributors later it forked 41 times on GitHub but after the Fortinet issue a Ransomware roundup series was all removed from GitHub.

Rackspace hit by Ransomware attack, Investigation going one it data were stolen.


December 2 2022 rackspace detected issue which is affecting the hosted exchange services and company shut sown the impacted services. Now it is confirmed that the failure was because of a ransomware attack.
"We appreciate your patience as we continue to work through the security issues that have affected our Hosted Exchange environment. As you know, on Friday, December 2nd, 2022, we became aware of suspicious activity and immediately took proactive measures to isolate the Hosted Exchange environment to contain the incident. We have since determined this suspicious activity was the result of a ransomware incident." Company said.

Compromised AIIMS Delhi server still Down from the last 6 days, hackers demand 200 crore in crypto


Aims Delhi server still down and now it is confirmed that it is ransomware attack as now hackers demanded 200 crore in cryptocurrency according to Livemint.

Nearly 40 million patients data record at risk including many reputed and public figures and AIIMS still have to work offline .

AIIMS Delhi server compromised, Delhi police start investigation


Delhi police IFSO unit register FIR regarding the recent AIIMS server compromise.AIIMS delhi told that multiple government agencies investigating this case.


AIIMS Delhi servers went offine at 7 AM wednesday and hospital informed the same to NIC and NIC working on restoring the system and all patient and emergency services managed manually.

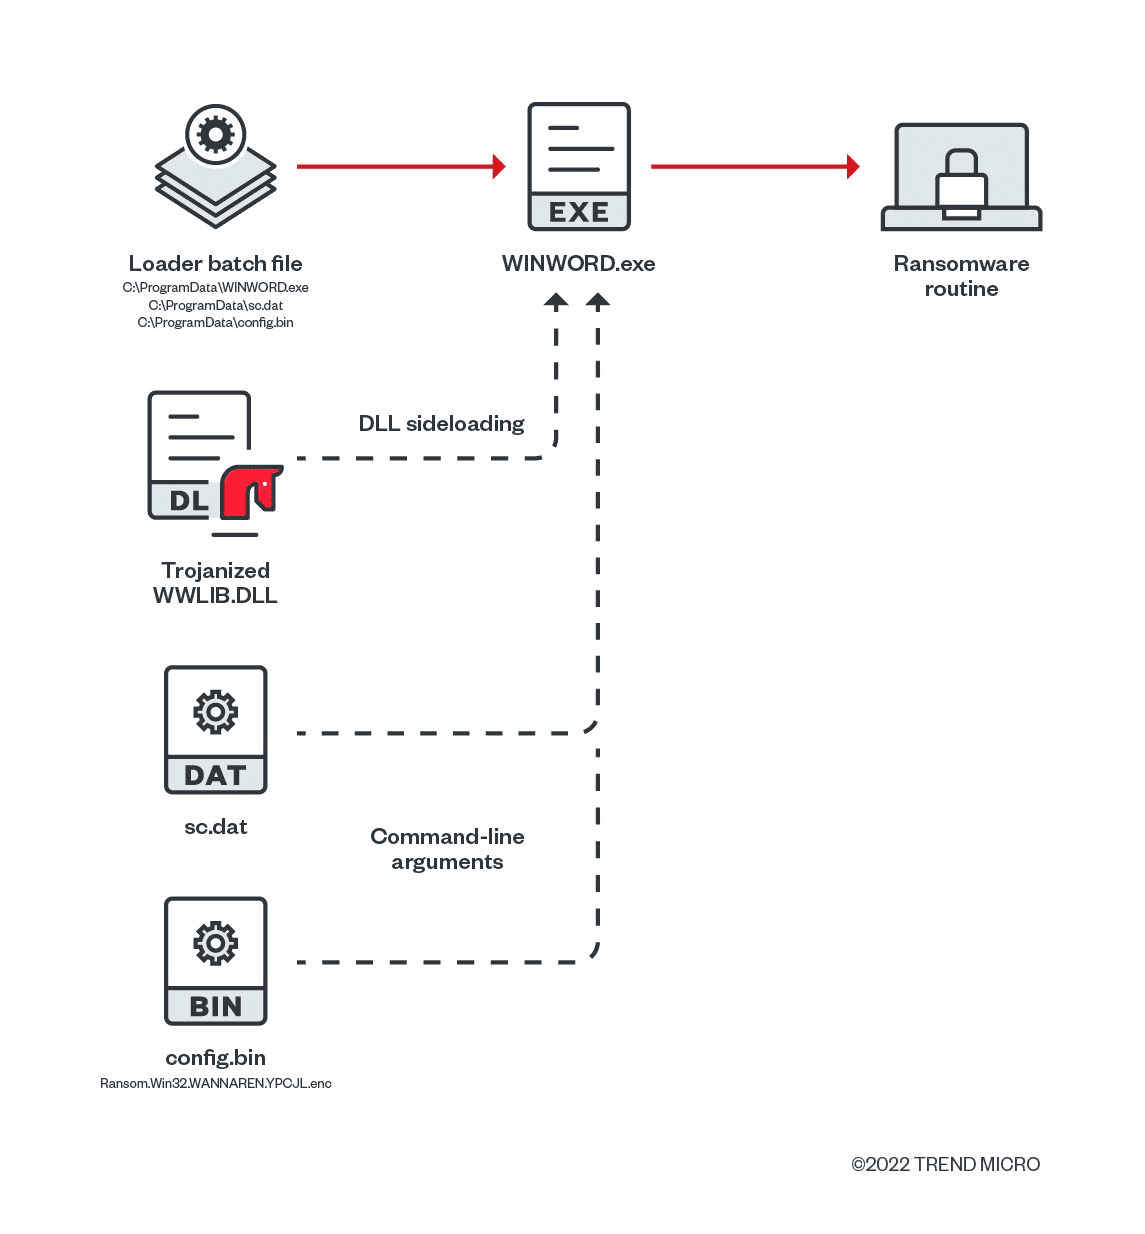
WannaRen, died in past reborn in present now targeting India

Credit: Trend-micro

Originally WannaRen discovered in 2020 when it is used against Chinese internet users. it is used for a very short time-span but damaged a lot in that short time than ransomware author shared the decryption keys to a security company in August 2020 and we believe that it was the end of WannaRen ransomware.

October 2022 Trend Micro team discovered "Life ransomware" which they believe may be a new variant of WannaRen. New Variant targeted Indian organizations .

Microsoft issued warning of a group of cyber criminal(DEV-0569) responsible for delivering Royal ransomware and other malware


Threat actor behind the development of ROYAL ransomware tracked by Microsoft as DEV-0569 mostly relies on malvertising, fake forum pages, phishing pages, blog comments. Microsoft team noticed continuous development and innovation of new attack vectors and defense evasion . These tactics allow the threat actor to increase the reach-ability .

Cyber attack in Vanuatu's government knocked offline from the last 11 days

According to civil servants who spoke to the BBC on condition of anonymity, it appears the government's servers were taken out on Friday 4 November.

Emails bouncing back from government addresses were the first sign something was wrong, residents said.

"If you take out the government internet… it affects everything. You want to do shipping? You've got to get stuff through approvals through customs. It affect airlines. It affects the health system - there isn't one bit of it that's unaffected," said Ms Stein.

1000 Medibank employees details also included in the hack

Now Medibank confirmed that around 1000 current and former staff details also included in the letest cyber hacking and we can see increased targeted scam attack. This time files which russian based hacker released containing names, email addresses, mobile phone number and device information. The insurer said it has received advice from experts that say the risk to the staff is low, but could result in highly targeted spam known as "spear fishing".

Sobeys supermarket chain hit by a Ransomware attack


Sobeys supermarket and pharmacy chain recovering from a ransomware attack.Sobeys Inc is the second largest supermarket chain in Canada, with over 1,500 stores operating across Canada under a variety of banners. Headquartered in Stellarton, Nova Scotia, it operates stores in all ten provinces and accumulated sales of more than C$25.1 billion in the fiscal 2019 operating year. It is a wholly owned subsidiary of Empire Company Limited, a Canadian business conglomerate.
It is a participant in the voluntary Scanner Price Accuracy Code managed by the Retail Council of Canada.

Hackers now release abortion related information after Medibank denied to pay ransom


The hackers who is behind the data breach of Australian health insurance provider Medibank which impact on 9.7 million people is now releasing private medical information on the dark web.

Mastermind already released file  “good list” and “naughty-list” on 09 November 2022 , here “naughty-list”include the details of those who had medical treatment for HIV, drug addiction or mental meath issues
Now hacker added one more file called “Boozy.csv” and wrote a blog post last Friday.

IT Software Firm Kaseya Hit By Supply Chain Ransomware Attack


Software maker Kaseya Limited is urging users of its VSA endpoint management and network monitoring tool to immediately shut down VSA servers to prevent them from being compromised in a widespread ransomware attack.

According to Kaseya, the attack began around 2PM ET on Friday. The company said that while the incident only appears to impact on-premises customers, SaaS servers have also been shut down as a precautionary measure.

New Ransomware 'Diavol' Linked to Notorious Cybercrime Gang


Wizard Spider, the notorious cybercrime gang that operated the TrickBot botnet and the Ryuk and Conti ransomware families, may have developed a new ransomware family, Fortinet reports.

Paytm Group Suffers a Massive Data Breach – Paytm Mall Hacked and Ransom Demanded


The Cybercrime markets keep surprising us with new events and at times, massive data breaches. But this time, cybleinc researchers stumbled on an interesting case.

Netwalker ransomware hit K-Electric, the major Pakistani electricity provider


K-Electric, the electricity provider for the city of Karachi, Pakistan, was hit by a Netwalker ransomware attack that blocked billing and online services.

University of Utah pays a $457,000 ransom to ransomware gang


The University of Utah admitted having paid a $457,059 ransom after the ransomware attack that took place on July 19, 2020, that infected systems on the network of the university’s College of Social and Behavioral Science [CSBS]). The university did not reveal the ransomware family involved in the attack.

Critical FFmpeg Vulnerability in Home Assistant: File Theft & Root Access Explained

  Critical Home Assistant FFmpeg Vulnerability Allows File Theft and Root Command Execution A newly disclosed security vulnerability in Home...